
“HIPAA compliant website” is not a certification.
A practice's obligations depend on who operates the site, what information it collects, where that information goes, which vendors can access it, and what safeguards and contracts are in place. TMN designs the marketing layer to minimize sensitive data collection and route scheduling or intake to systems the practice has approved.
What HIPAA actually covers.
A plain-language orientation, not legal advice. Your privacy officer and counsel govern your obligations, and this page is written to help you ask them better questions.
It governs regulated relationships and information
HIPAA applies to covered entities and, when the rule's conditions are met, their business associates. There is no federal “HIPAA compliant website” certification. A badge cannot establish that a practice's data flows, safeguards, vendor relationships, and contracts satisfy its obligations.
Protected health information is the line
PHI is individually identifiable health information held or transmitted by a covered entity or business associate. HHS cautions that information collected from patients or prospective patients on a regulated entity's site can be PHI. A form asking for symptoms, insurance details, or an appointment reason requires a careful data-flow review.
Business associate agreements
A vendor that creates, receives, maintains, or transmits PHI on a practice's behalf may be a business associate and require a BAA. The agreement matters, but it does not replace appropriate configuration, access controls, security safeguards, and an accurate understanding of every destination the data reaches.
Tracking technologies drew the scrutiny
HHS says tracking technologies on authenticated pages generally have access to PHI. Its bulletin also notes that a 2024 court order vacated part of its guidance on IP addresses and visits to unauthenticated public pages. Some unauthenticated scheduling and symptom flows may still disclose PHI. Cookie banners do not create HIPAA authorization.
How TMN builds around it.
The design goal is to keep the public marketing layer narrow, understandable, and easy for the practice and its advisors to review.
Collect only what the practice approves
Public forms should not invite symptoms, diagnoses, insurance details, or treatment history unless the practice has deliberately approved the workflow and its safeguards. Even a short contact form needs an accurate review of what is collected, why, and where it goes.
Intake routes to practice-selected systems
Scheduling and intake can link to or embed the systems your practice has selected when that work is in scope. The practice and its advisors confirm the vendor relationship, BAA status when applicable, configuration, access, retention, and downstream data handling.
Analytics you choose deliberately
TMN can implement a minimal analytics configuration or omit analytics entirely. Any pixel, session replay, call-tracking, advertising, or measurement tool should be reviewed against the actual page, data elements, vendor terms, and practice requirements before launch.
Clinical content stays yours
Treatment pages are prepared for the practice's review and published only after its clinical approval. The live LumiClinics SPRAVATO page includes published Indications and Important Safety Information alongside a route to the practice's intake system. TMN does not independently approve medical claims.
Crisis resources prepared for clinical review
988 and local crisis resources can be made visible where the practice's clinical reviewers require them, with approved language distinguishing the site from an emergency channel.
Hand-coded, few moving parts
Every plugin is another vendor touching your site. A hand-coded static site has a smaller surface to reason about than a plugin stack that updates itself on someone else's schedule.
Healthcare practices, publicly credited.
Live sites on client domains that credit TMN, so you can check the work rather than take a claim.
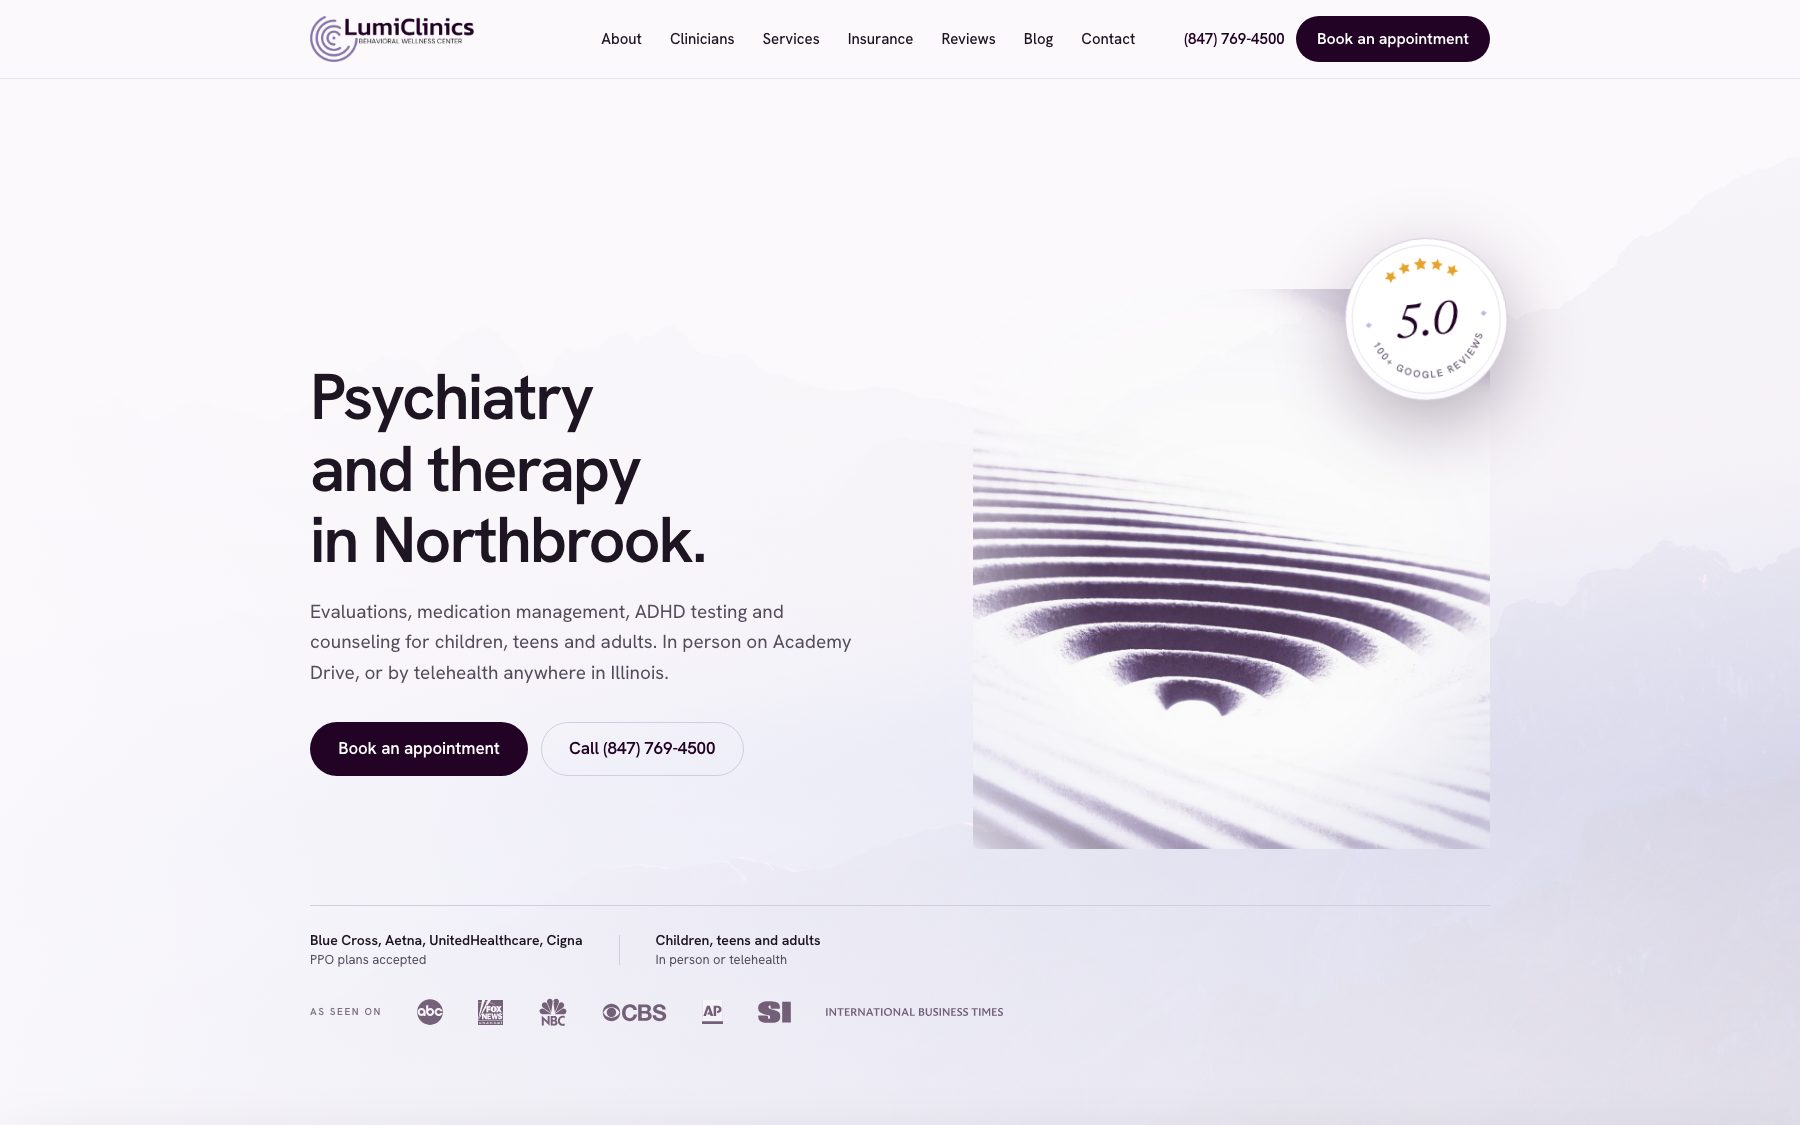
LumiClinics
Psychiatry and therapy practice in Northbrook, Illinois, serving patients statewide by telehealth. Named providers, plain-language insurance, one direct intake path, and regulated treatment content. Case study.
Training Wheels ABA
Pediatric ABA therapy group with 3 clinic locations in Austin, Texas. Insurance clarity including Medicaid, simple tour scheduling, and hiring pages that support clinician recruiting. Case study.
Smitha Reddy MD
Rheumatology and functional medicine practice in San Diego, built credential-forward with the patient path routed to the affiliated care organization. Case study.
What practice owners ask first.
Is my website HIPAA compliant?
There is no federal certification that makes a site compliant on its own. The answer depends on the practice, data flows, vendors, safeguards, and contracts. A business associate agreement (BAA) can be required, but it is only one part of the analysis. Confirm your specific posture with your privacy officer and counsel.
Can a website contact form be HIPAA compliant?
It can be, but the answer depends on the regulated entity, information collected, purpose, and every system that receives it. HHS says individually identifiable health information collected on a regulated entity's site generally is PHI. TMN keeps public forms narrow and routes clinical intake only through practice-approved workflows.
Can I use Google Analytics or a Meta pixel on a medical website?
Only after a page-by-page and data-flow review. HHS says tracking technologies on authenticated pages generally have access to PHI. It also notes that a 2024 court order vacated part of its guidance on IP addresses and visits to unauthenticated public pages. Some unauthenticated scheduling and symptom flows may still disclose PHI. A cookie banner does not by itself resolve the HIPAA analysis.
Does a web designer need to sign a BAA?
It depends on the scope. If a designer creates, receives, maintains, or transmits PHI on the practice's behalf, business-associate obligations may apply. TMN identifies proposed access and data handling before work begins so the practice and its advisors can determine the required contract and safeguards.
How much does a HIPAA-aware practice website cost?
TMN's published starting prices are $2,250 for a Starter Refresh, $3,750 for a Full Site Rebuild, and $5,000+ for a Custom Studio Build. Any specialized privacy, security, vendor, or integration scope is identified before the final price is confirmed. See full pricing detail.
Is this page legal advice?
No. This page is a plain-language orientation to help you ask your privacy officer and counsel better questions. They govern your obligations, and nothing here substitutes for their review of your specific practice.
Ready to get started?
Tell us about your operation. We’ll put together a free custom homepage so you can see the direction before committing. No retainer. No pressure.